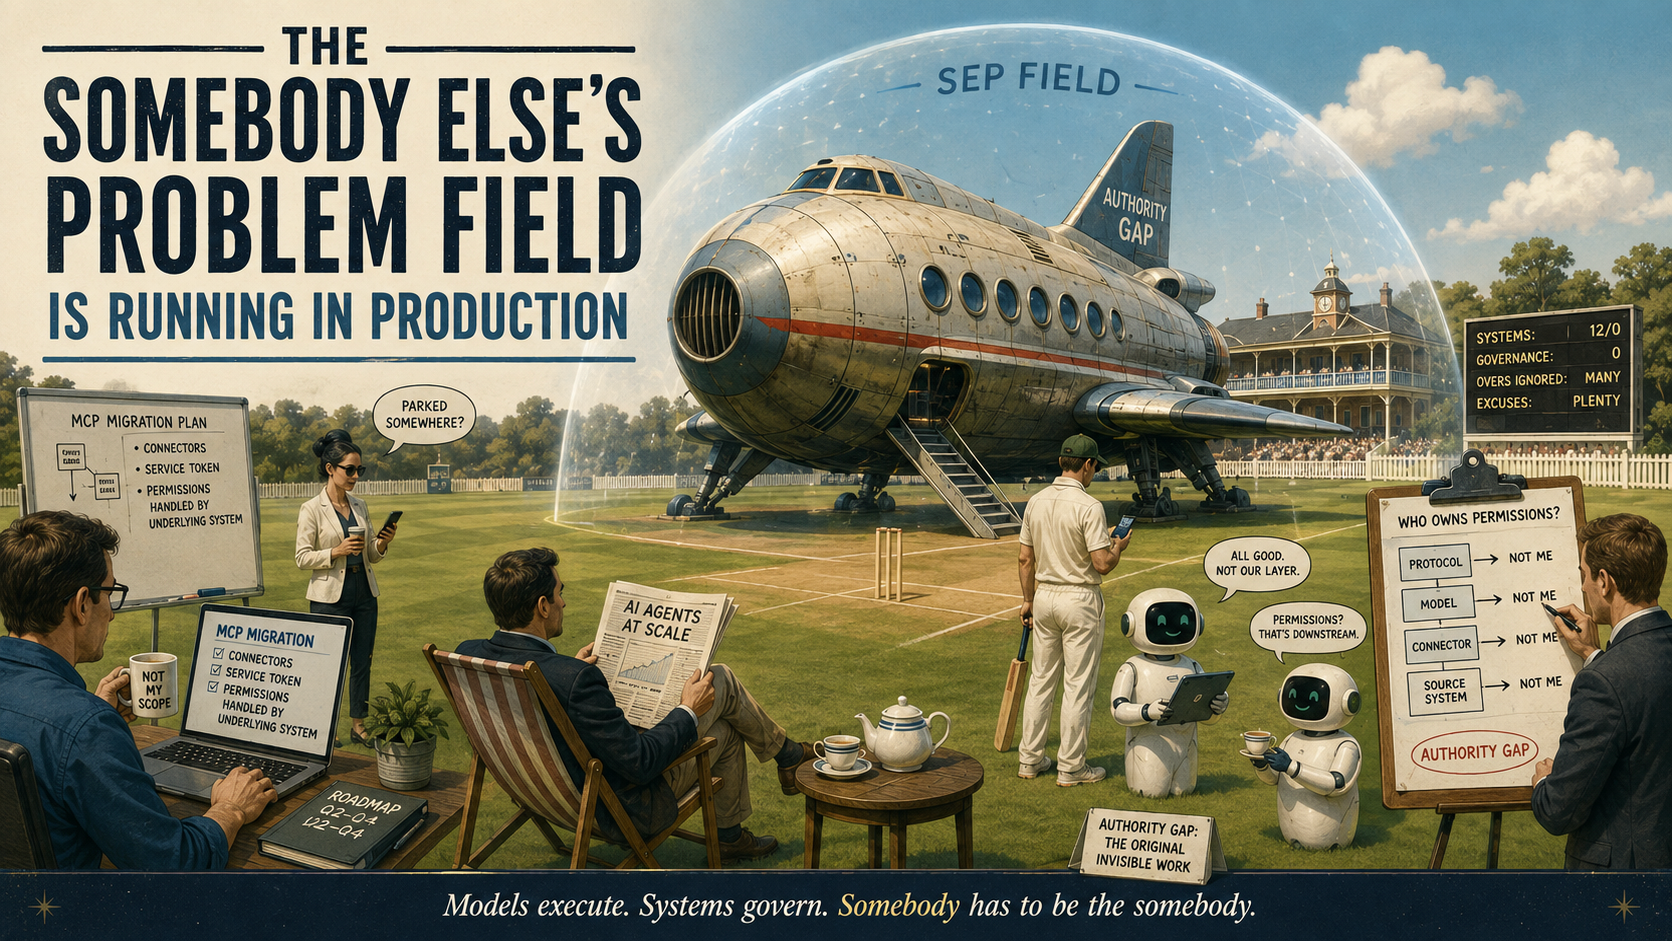
Douglas Adams gave us the cheapest cloaking device in science fiction: the Somebody Else’s Problem field. It doesn’t make a thing invisible. It relies on the observer’s own unwillingness to see something inconvenient, unexpected, or unexplainable. The brain edits it out. A whole spaceship can sit in the middle of a cricket pitch, unnoticed, because everyone who looks at it decides it’s not theirs to deal with.
The AI agent ecosystem has deployed one at scale. It’s wrapped around a specific question: what happens to authority after an authorized request succeeds.
The tell
This week’s example, via The New Stack: Mistral is shutting down the Google Drive and SharePoint Knowledge Connectors in Vibe Work on August 31 and pointing enterprise customers at MCP-based replacements. No automatic migration. And — this is the part that matters — Mistral doesn’t operate the third-party MCP servers behind the replacements, so it makes no commitments about how they retrieve documents, what they cache, or whether search results will be permission-filtered the way the outgoing index was. The retrieval architecture is unspecified. The deletion timeline for the existing index is unspecified.
Let’s be precise about what is and isn’t defined here, because the obvious rebuttal is “MCP has OAuth — read the spec.” It does. MCP is not permissionless: it carries an OAuth 2.1-based authorization specification, recently hardened by a batch of protocol changes, and as of June 2026 a stable Enterprise-Managed Authorization extension that makes the organization’s identity provider the authoritative decision-maker for which MCP servers a user can reach. An active interest group is evolving it further. That work is real, and it governs something specific: how a client establishes and presents delegated access to a server.
What remains undefined is the end-to-end authority semantics: whether source-level permissions survive retrieval, caching, indexing, transformation, retention, revocation, and later disclosure. OAuth can authorize the request. It does not govern the information after the request succeeds. Mistral’s migration documentation does not fill that gap — it explicitly hands the behavior to connector operators it doesn’t control.
So the plumbing standardizes on a hard deadline, connection authorization matures alongside it, and the information-lifecycle authority layer ships as an open question.
This isn’t a Mistral problem. It’s the pattern everywhere MCP-ification is happening — and the reason is structural, not negligent. End-to-end permission semantics lag behind transport interoperability because interoperability benefits every participant, while lifecycle accountability crosses all of their boundaries. So the ecosystem converges on a division of labor nobody signed:
- The protocol says: here’s how to move the data, and here’s how to authorize the connection.
- The model says: I execute what I’m given.
- The connector operator says: we pass through whatever the source system allows.
- The source system says: we enforced permissions at our boundary; downstream is out of scope.
Every component can be locally correct while the resulting system is globally unauthorized. That’s the whole problem in one sentence. Protocol correctness plus connector correctness plus model correctness plus source-system correctness does not compose into governance correctness — because identity, purpose, time, delegation, derivation, and revocation semantics can change at every boundary while each participant reasons only about its own. Permission propagation is not authority preservation.
And notice what that means for ownership: many parties own fragments of the authority problem. No party is accountable for the composed result. That’s why adding more locally responsible actors doesn’t solve it — and it’s why the SEP field forms without anyone behaving negligently. The architecture itself invites each party to reason about its own boundary, and the composed question belongs to no one’s contract.
The law already named the failure mode this becomes
Law has a useful term for structuring your process so an inconvenient fact never lands on your desk: willful blindness — the deliberate avoidance of knowledge you have reason to believe exists. The doctrine’s exact requirements vary by context, and I’m not claiming any given MCP permission gap satisfies it. The analogy is structural — and the structure has a trajectory.
At first, this is fragmentation: each party genuinely reasoning within its own contract. But once the gap is known and production deployment continues without anyone being assigned end-to-end accountability, fragmentation hardens into something that begins to resemble willful blindness. “Permissions are handled by the underlying system” is the load-bearing sentence in a hundred integration docs, and it does the same work as the SEP field: it doesn’t answer the question, it makes the question disappear from view. Legal systems have long experience with actors who engineer their own ignorance, and their consistent response is to refuse to reward it.
The scenario that isn’t just IAM
Here’s the version of the problem that survives the “that’s just misconfigured RBAC” objection.
Alice legitimately authorizes an agent to ingest a document. It gets indexed, embedded, summarized, folded into agent memory and derived artifacts. Months later, Alice’s permissions change — she leaves the team, the deal closes, the matter becomes privileged. An agent operating for Bob later retrieves a summary derived from that document.
Alice’s original acquisition was authorized. Bob’s later disclosure was not. And yet every component may have followed its local contract to the letter — the retrieval layer had no locally represented rule telling it otherwise. No component violated the authority it knew about. The composed system failed to preserve authority it had never represented end to end. That’s the failure: no contract carried Alice’s changing authority into the derived state.
The Mistral migration sharpens this rather than causing it. The outgoing connector at least documented a periodically synchronized replica of source permissions — not live authority, but a defined governance mechanism with known staleness. Under the MCP replacements, retrieval, caching, permission filtering, and deletion become connector-specific behaviors that Mistral does not control or guarantee. The temporal problem was always there; what’s being retired is the documented answer to it.
An MCP server can perfectly enforce today’s SharePoint ACL and still not answer for yesterday’s information sitting in an embedding store, a graph, a cache, a memory, a summary. Authority to ingest is not perpetual authority to retain, derive from, retrieve, or disclose.
Models execute. Systems govern. Somebody has to be the somebody.
The fix isn’t a better model, and it isn’t only a richer protocol. An authorization decision is not a gate crossed once at retrieval time — it’s an obligation that must remain attached to information through copying, memory, derivation, revocation, substrate change, and disclosure. That obligation has to live in a layer that is nobody else’s problem: an external system whose entire job is to hold the questions the SEP field hides:
- Who is this agent acting as, right now? Not what token it holds — what authority was delegated, by whom, with what scope.
- What did the permission state look like at the moment of access? Evidence, not vibes. If the answer isn’t recorded, it isn’t governed.
- What authority exists now to retain, retrieve, derive from, or disclose what was accessed then? Access is an event; retention is a state. Governing the event and ignoring the state is how the Alice-and-Bob disclosure happens.
- What happens when the substrate changes underneath? A connector migration is an authority event, not a plumbing event. Indexed data from the old regime doesn’t inherit legitimacy in the new one.
None of this is exotic. It’s the same discipline every regulated industry already applies to human actors. The only novel part is admitting that agents need it too — which requires switching off the field and looking directly at the ship parked on the pitch.
There’s a small irony worth savoring here. The protocol community’s formal mechanism for closing recognized gaps is called a SEP — a Specification Enhancement Proposal. So the gaps that get seen have a path to getting fixed. The problem is everything that happens while production keeps running inside the other kind of SEP field.
The uncomfortable truth about that field is that it’s cheap to run and expensive to switch off. Every vendor that names the composed authority gap inherits it. So the market’s equilibrium is collective squinting — right up until the first incident large enough that a customer, an auditor, or a court refuses to not-see it. When that happens, “each component followed its contract” will get exactly the reception engineered ignorance always gets.
The ship is on the pitch. It’s been there the whole time.
Why locally correct authority decisions fail to compose into globally governed behavior — and why authorization must be preserved and reevaluated across the information lifecycle, not checked once at access — is explored in the forthcoming Governance Fidelity Theory paper.
Part of a series on AI governance in regulated-data platforms: The Fireworks Phase, We’ve Been Choosing the Wrong Container for 35 Years, Authority Must Live Outside the Model, and The Drift Machine Is the Problem, Not the Filename.